Printable Exams-in PDF format
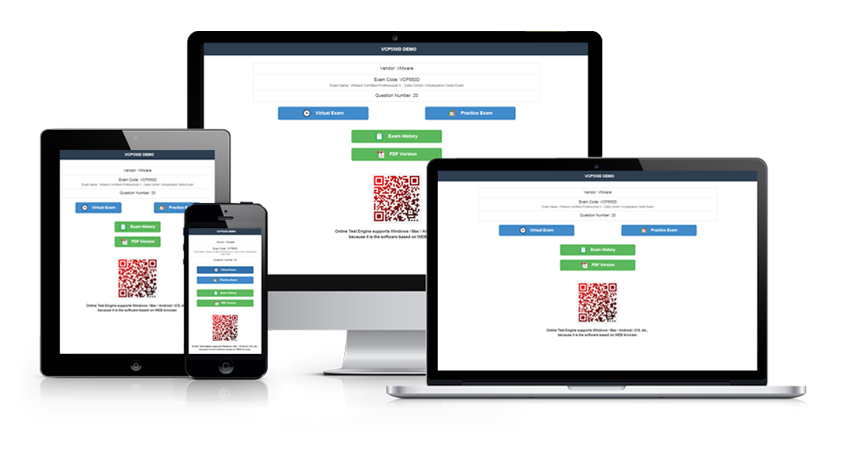
The pdf format is the common version of our Certified in Risk and Information Systems Control (CRISC日本語版) pdf training material.The content is the same as other two versions. Besides, the cost of CRISC日本語 pdf test torrent is very reasonable and affordable. Certified in Risk and Information Systems Control (CRISC日本語版) sure pass pdf can be printed into paper, which is very convenient for you to review and do marks. If you are tired of the digital screen study and want to study with your pens, Certified in Risk and Information Systems Control (CRISC日本語版) pdf version is suitable for you. The Isaca Certificaton CRISC日本語 pdf paper study material is very convenient to carry. You can make full use of your spare time to prepare the Certified in Risk and Information Systems Control (CRISC日本語版) actual test. When you are at the cafe, you can read and scan your papers and study two questions. I think this way to study is acceptable by many people. In addition, when you want to do some marks during your Certified in Risk and Information Systems Control (CRISC日本語版) test study, you just need a pen, you can write down what you thought. With the obvious marks, you will soon get your information in the next review. Then repeated memory about CRISC日本語 pass4sure study guide will bring a good score in the Certified in Risk and Information Systems Control (CRISC日本語版) actual test.
As we all know, Certified in Risk and Information Systems Control (CRISC日本語版) certification increasingly becomes a validation of an individual's skills. Now, the market has a great demand for the people qualified with Certified in Risk and Information Systems Control (CRISC日本語版) certification. In recent years, the ISACA Isaca Certificaton certification has become a global standard for many successfully IT companies. So, in order to get a better job chance, many people choose to attend the Certified in Risk and Information Systems Control (CRISC日本語版) exam test and get the certification. Now, there are many people preparing for the CRISC日本語 test, and most of them meet with difficulties. How to prepare it with high efficiency is quite important. While, your problem will be solved by the Certified in Risk and Information Systems Control (CRISC日本語版) test practice material which can ensure you 100% pass.

Risk Response Mitigation: 23%
- Discuss with the risk owners to choose and align proposed risk responses with the business objectives to allow for informed risk decision making;
- Consult with the stakeholders on design, implementation, or adjustment in mitigation controls to ascertain that risks are managed to a certain acceptable level;
- Discuss with or help the risk owners on risk action development plans to incorporate key elements in development plans;
- Help the control owners to develop control mechanisms and documentation for effective and efficient control execution;
- Revise a risk register to include changes in risk and risk response management;
- Certify the execution of risk responses based on risk action plans.
- Establish the options for risk response and measure their risk management effectiveness and efficiency in alignment with the business objectives;
Reference: http://www.isaca.org/certification/crisc-certified-in-risk-and-information-systems-control/pages/default.aspx
ISACA Risk and Information Systems Control Exam Syllabus Topics:
| Topic | Details | Weights |
|---|
| Information Technology and Security | A. Information Technology Principles- Enterprise Architecture
- IT Operations Management (e.g., change management, IT assets, problems, incidents)
- Project Management
- Disaster Recovery Management (DRM)
- Data Lifecycle Management
- System Development Life Cycle (SDLC)
- Emerging Technologies
B. Information Security Principles - Information Security Concepts, Frameworks, and Standards
- Information Security Awareness Training
- Business Continuity Management
- Data Privacy and Data Protection Principles
| 22% |
| Risk Response and Reporting | A. Risk Response- Risk Treatment / Risk Response Options
- Risk and Control Ownership
- Third-Party Risk Management
- Issue, Finding, and Exception Management
- Management of Emerging Risk
B. Control Design and Implementation - Control Types, Standards, and Frameworks
- Control Design, Selection, and Analysis
- Control Implementation
- Control Testing and Effectiveness Evaluation
C. Risk Monitoring and Reporting - Risk Treatment Plans
- Data Collection, Aggregation, Analysis, and Validation
- Risk and Control Monitoring Techniques
- Risk and Control Reporting Techniques (heatmap, scorecards, dashboards)
- Key Performance Indicators
- Key Risk Indicators (KRIs)
- Key Control Indicators (KCIs)
| 32% |
| IT Risk Assessment | A. IT Risk Identification- Risk Events (e.g., contributing conditions, loss result)
- Threat Modelling and Threat Landscape
- Vulnerability and Control Deficiency Analysis (e.g., root cause analysis)
- Risk Scenario Development
B. IT Risk Analysis and Evaluation - Risk Assessment Concepts, Standards, and Frameworks
- Risk Register
- Risk Analysis Methodologies
- Business Impact Analysis
- Inherent and Residual Risk
| 20% |
| Governance | A. Organizational Governance- Organizational Strategy, Goals, and Objectives
- Organizational Structure, Roles, and Responsibilities
- Organizational Culture
- Policies and Standards
- Business Processes
- Organizational Assets
B. Risk Governance - Enterprise Risk Management and Risk Management Framework
- Three Lines of Defense
- Risk Profile
- Risk Appetite and Risk Tolerance
- Legal, Regulatory, and Contractual Requirements
- Professional Ethics of Risk Management
| 26% |
Exam Syllabus
The ISACA CRISC exam is aimed at those professionals who want to build a career in the field of IT and, in particular, in the risk management domain. The test validates that the candidates possess the basic knowledge and skills in the area of risk and information systems control. The topics covered in the exam are highlighted below:
Information Technology Risk Identification: 27%
- Develop in-depth IT risk scenarios according to available data to establish potential effects on the enterprise objectives and operations;
- Identify possible vulnerabilities and threats to people, process, and technology of an organization;
- Create an IT risk register for documenting an identified IT risk scenario and incorporate the same in the risk profile of the enterprise;
- Partner in developing a risk awareness program and carry out the required training to educate the stakeholders on the risk potential and promote the organizational risk-aware culture;
- Gather and analyze information, such as existing documentation to identify possible IT risk or its impact on the business operations and objectives of an organization;
- Identify the domain of IT risk and contribute to the IT risk management strategy execution to support the business objectives while aligning with the enterprise risk management strategy;
- Recognize risk appetite and tolerance as defined by the key stakeholders and senior leadership to align with the business objectives.
We offer free update service for one year
Every time, before our customer buying our Certified in Risk and Information Systems Control (CRISC日本語版) pass4sure practice, they always ask whether it is the latest or not, and care about the latest update time. It is very normal. We can understand this case. First, we guarantee the Certified in Risk and Information Systems Control (CRISC日本語版) test dumps you get are the latest and valid which can ensure you pass with ease. Second, we offer free update service for one year after you purchase Isaca Certificaton sure pass pdf, so you do not worry the dump is updated after you buy. If there is any update about CRISC日本語 Certified in Risk and Information Systems Control (CRISC日本語版) test practice material, our system will send it to your payment email automatically. Besides, if you care about the update information, you can pay attention to the version No. on our product page. If the version No. is increased, the Certified in Risk and Information Systems Control (CRISC日本語版) pdf dump is updated. If you do not receive any email when you find our dumps are updated, please contact us by email, we will solve your problem as soon as possible.
Besides, we have the full refund policy, if you do not pass the ISACA Certified in Risk and Information Systems Control (CRISC日本語版) actual test, we promise to give you full refund. You just need to show us your failure Certified in Risk and Information Systems Control (CRISC日本語版) certification. After confirmation, we will refund you. The refund money will enter into your accounts in about 15 days, so please wait with patience.
Instant Download CRISC日本語 Braindumps: Our system will send you the TestPDF CRISC日本語 braindumps file you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)


 PDF Version Demo